Container-based development
Give each of your development tools, including AI coding agents, its own secure network space - so an agent that touches your code can never reach the rest of your systems.
An AI coding agent needs your code. It doesn’t need a way into your internal servers, your databases, or your login details for other systems.
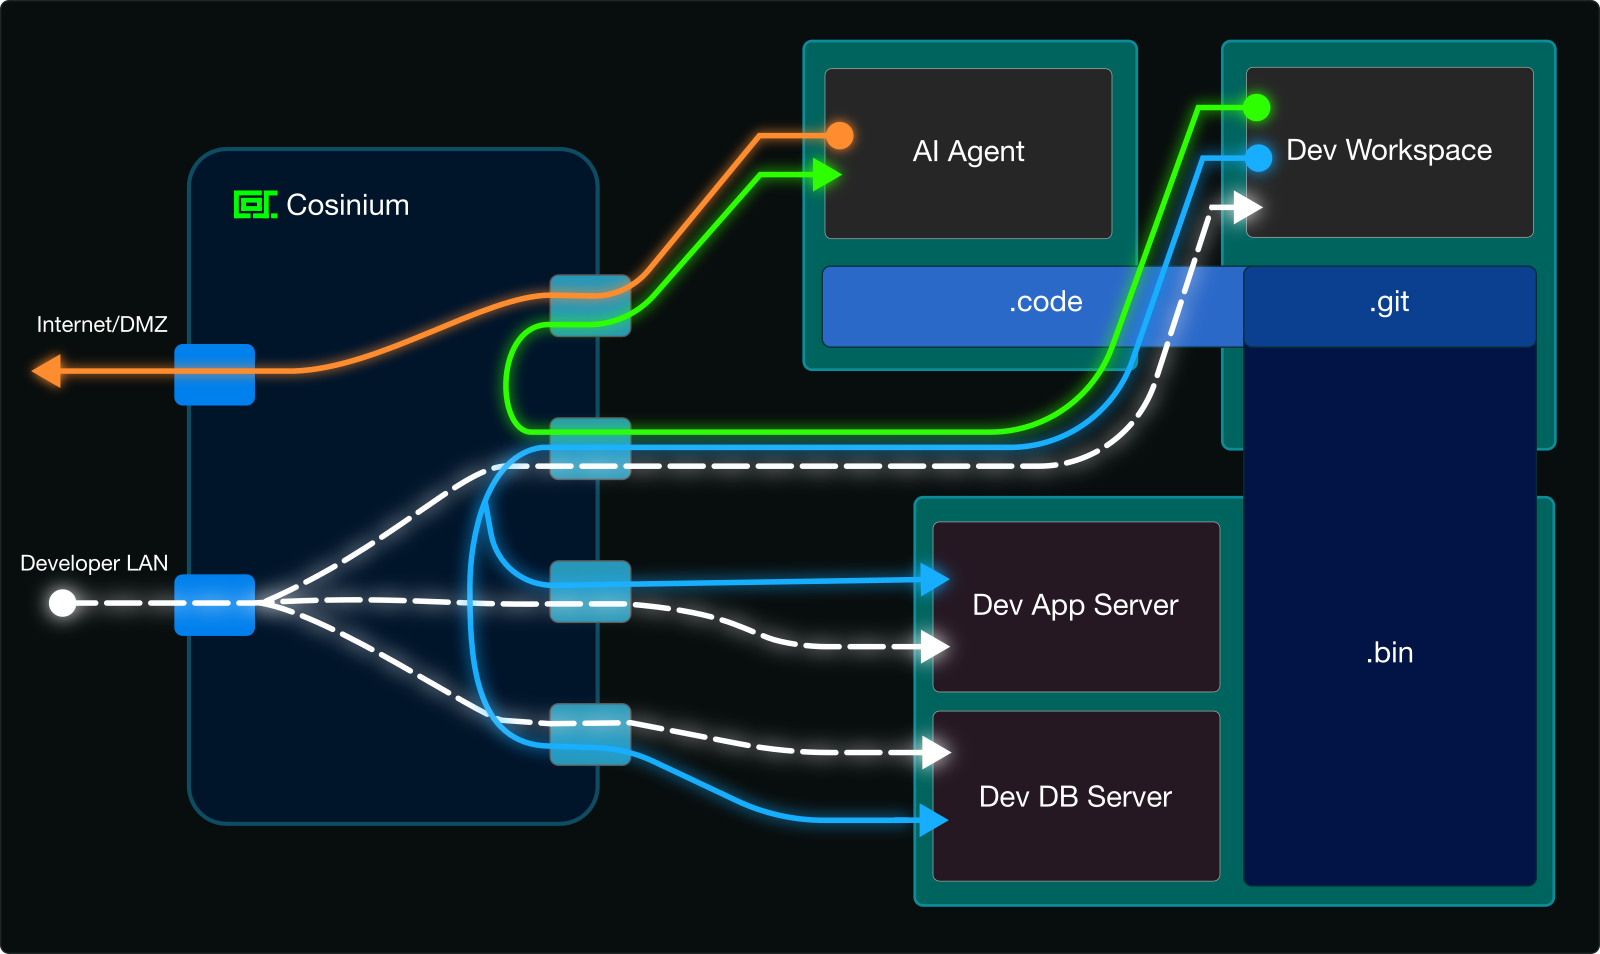
Run Cosinium as a container-based firewall, and you can give every container its own network space, with full control over what it can reach. Every running instance in the illustration below is an individual container.
How it works
The AI agent gets a copy of your code and nothing else. It has no route to your office network or to anything beyond the firewall rules you set.
Your own developer workspace container has a direct mapping to that code, along with being able to push commits and build binaries for CI/CD. Cosinium sets up a private connection between the two containers, so you can guide agent’s work without putting both containers on the same open network.
Your development servers stay easy to reach - from your regular computer and from inside your workspace container.
Every connection between these pieces goes through Cosinium’s firewall. Each connection is one you chose to allow.